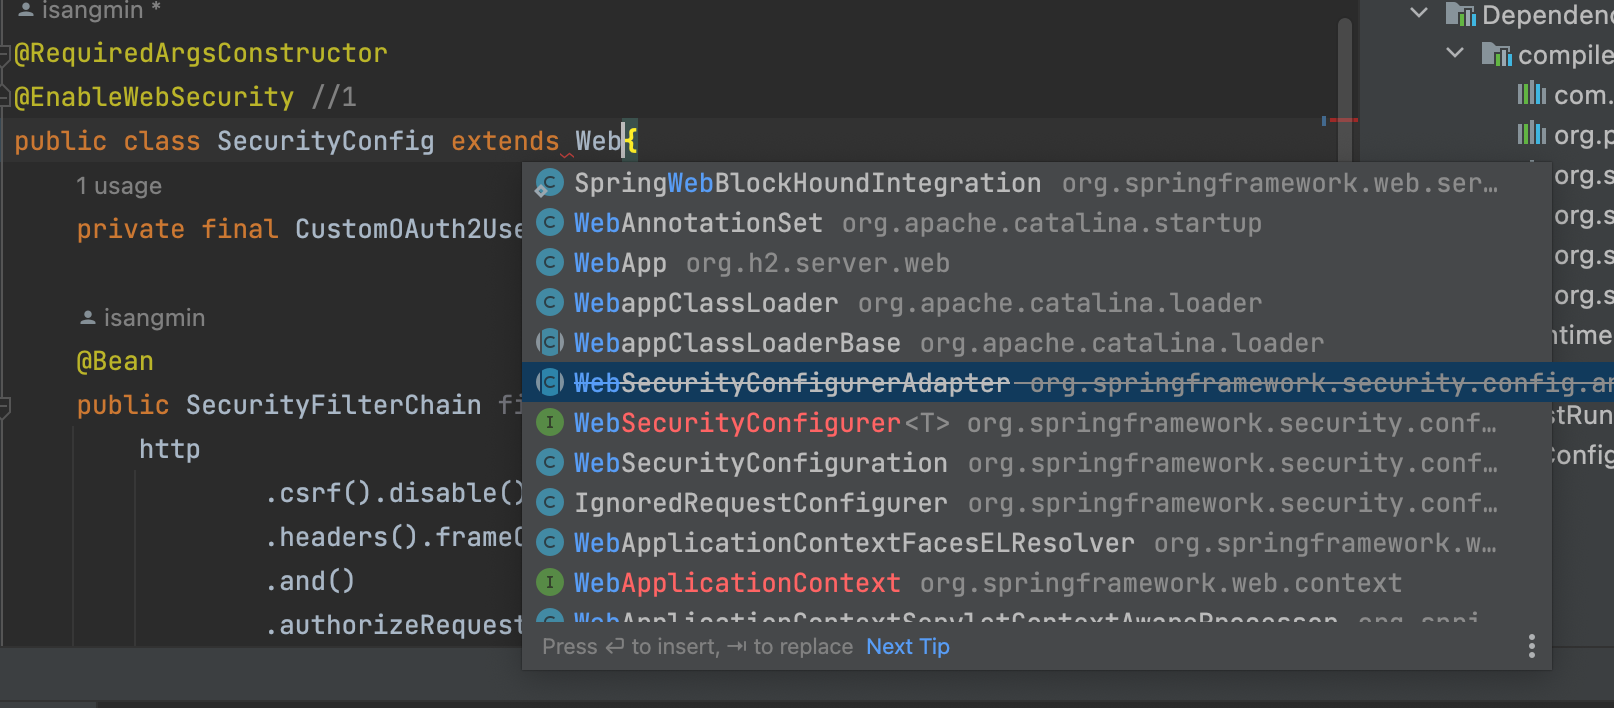
스프링 버전이 올라가면서 WebSecurityConfigurerAdapter 에도 deprecate인 모습

SecurityFilterChain Bean을 사용하여 HttpSecurity를 구성, WebSecurityCustomizer Bean을 사용하여 WebSecurity를 구성하도록 안내하고 있다.
찾아보니,
이제부터는 @Bean으로 등록하고 SecurityFilterChain을 반환하면 됩니다.
지금 하고 있는 코드를 예로 들면,
@RequiredArgsConstructor
@EnableWebSecurity
public class SecurityConfig extends WebSecurityConfigurerAdapter {
    private final CustomOAuth2UserService customOAuth2UserService;

    @Override
    protected void configure(HttpSecurity http) throws Exception {
        http
                .csrf().disable()
                .headers().frameOptions().disable()
                .and()
                    .authorizeRequests()
                    .antMatchers("/","/css/**","/images/**","/js/**","/h2-console/**").permitAll()
                    .antMatchers("/api/v1/**").hasRole(Role.USER.name())
                    .anyRequest().authenticated()
                .and()
                    .logout()
                        .logoutSuccessUrl("/")
                .and()
                    .oauth2Login()
                        .userInfoEndpoint()
                            .userService(customOAuth2UserService);
    }
}
이렇게 되어있는 코드를
@RequiredArgsConstructor
@EnableWebSecurity //1
public class SecurityConfig {
    private final CustomOAuth2UserService customOAuth2UserService;

    @Bean
    public SecurityFilterChain filterChain(HttpSecurity http) throws Exception {
        http
                .csrf().disable()
                .headers().frameOptions().disable() //2
                .and()
                .authorizeRequests() //3
                .antMatchers("/","/css/**","/images/**","/js/**","/h2-console/**").permitAll()
                .antMatchers("/api/v1/**").hasRole(Role.USER.name()) //4
                .anyRequest().authenticated()//5
                .and()
                .logout()
                .logoutSuccessUrl("/")//6
                .and()
                .oauth2Login()//7
                .userInfoEndpoint()//8
                .userService(customOAuth2UserService);//9
        return http.build();
    }
}
이렇게하면 된다.


댓글